One Page Risk Appetite Statement for Boards: Templates & Checklist
A risk appetite statement is a short, board approved policy that defines the types and amount of risk the board permits management to take in pursuit of strategy. If your board does not have one, the next board meeting is a good time to bring a one page draft. The rest of this article shows you how to build one that holds up under real scrutiny, with measurable tolerances instead of vague reassurance.
TL;DR:
A risk appetite statement should clearly link strategic goals to acceptable risk levels, translating broad language into specific metrics for operational use.
Quantitative thresholds, such as loss limits or uptime targets, are essential for monitoring and should align with existing management reporting units.
The board must approve the statement and review it annually, with management responsible for cascading tolerances and recording breaches or exceptions.
Effective communication involves integrating the risk policy into daily workflows and maintaining a breach log to facilitate quick responses and regulatory compliance.
A well-maintained, actionable risk appetite document requires ongoing oversight, ownership, and regular updates to stay connected to decision-making processes.
Chief Legal Officechieflegaloffice.comKeep Board Risk Decisions MovingChief Legal Office helps growing technology companies organize governance, enterprise risk, and legal work around the decisions ahead.Learn about Chief Legal Office
Table of Contents
Why your board needs a risk appetite statement
What goes in a board approved risk appetite statement
Turning appetite into numbers you can monitor
Sample language your board can actually use
Who approves it and how often should the board review it
Communicating the statement and handling breaches
Why most risk appetite statements end up as shelfware
Putting it on one page for your board
Getting your statement from draft to board ready
FAQ
Sources
Why your board needs a risk appetite statement
Here is the problem I see over and over. A company grows fast, the board gets bigger, and suddenly five smart people have five different opinions about how much risk the company should take. Nobody has written it down. So every decision, whether to enter a new market, change a pricing model, or accept a customer with weak credit, turns into a fresh argument instead of a quick check against an agreed standard.
That is what a risk appetite statement fixes. It is not a legal formality. It is the document that lets your CEO and CFO make fast decisions without calling an emergency board meeting every time something interesting comes up.
COSO’s enterprise risk management guidance frames risk appetite as the amount and type of risk an organization will accept in pursuit of value, directly tied to strategy. That framing matters because it puts the statement upstream of your strategic plan, not as an afterthought bolted on after the plan is set. If your appetite statement does not connect to how you actually make money, it will sit in a drawer.
Banking regulators treat this as a governance expectation, not a nice to have. The FDIC’s guidelines on corporate governance and risk management call for boards of larger, complex institutions to approve a risk profile and risk appetite statement, and to maintain a three line of defense model with clear reporting when the business breaches its limits. You may not run a bank, but examiners, investors, and increasingly insurers are borrowing this same checklist when they evaluate your governance maturity.
What happens without one? A few patterns show up constantly:
Leadership says yes to a large customer concentration because nobody defined an acceptable limit, and then panics when that customer churns.
A product team ships a feature with real privacy exposure because legal and engineering never agreed on where the line sits.
The board discovers a material risk only after it becomes a headline, instead of through a routine report.
None of these are failures of intelligence. They are failures of documentation. A clear statement turns “we should probably be careful” into something the whole company can act on consistently.
What goes in a board approved risk appetite statement
A good statement is short enough to read in two minutes and specific enough that two different managers would make the same call when they apply it. Here is the structure that auditors, regulators, and frankly most boards expect to see.
An overarching appetite sentence. One or two sentences tying risk taking directly to strategy and mission. Something like: “The company accepts moderate operational risk and low legal and regulatory risk in pursuit of sustainable, profitable growth.”
Risk categories. List the categories that matter to your business: strategic, financial, operational, legal and regulatory, reputational, cyber and technology. For each one, say whether the board’s language is qualitative (low, moderate, high) or quantitative (a specific ratio or dollar band).
Tolerance thresholds and limit types. This is where the statement becomes usable. Translate each qualitative band into a number: a loss threshold, a concentration cap, an uptime target.
Escalation triggers and exception handling. Define what happens when a business unit wants to exceed its tolerance. Who approves the exception, and for how long.
Reporting expectations and review cadence. State how often management reports against the statement and how often the board reviews the statement itself.
COSO’s guidance notes that boards should expect both a high level appetite statement and a set of cascaded tolerances underneath it, and that most organizations start broad and narrow the language as the program matures. Do not try to write the perfect quantified version in year one. Write something true and simple, then tighten it.
The distinction between appetite and tolerance trips up a lot of boards, so it is worth being precise. Wolters Kluwer’s explanation of risk appetite versus risk tolerance describes appetite as strategic and broad, while tolerance is tactical and measured in the actual units of the objective, whether that is dollars, days, or defect rates. Appetite tells you the direction. Tolerance tells you exactly where the fence is.
Pro Tip: Write your tolerance thresholds in the same units your management team already tracks monthly, so the statement plugs into existing dashboards instead of requiring a new reporting system.
Turning appetite into numbers you can monitor
A statement that says “we have low appetite for legal risk” is a start, but it does not tell anyone what to do on a Tuesday. The real work is translating qualitative bands into metrics a business unit can actually watch.
Not every category needs a number. Reputational risk, for instance, often stays qualitative because it resists clean measurement. But most operational and financial categories can and should be quantified:
Financial loss bands. A maximum acceptable loss from a single vendor failure or fraud event, expressed as a dollar figure or a percentage of revenue.
Capital or liquidity ratios. Common in regulated industries, these set a floor below which management must act.
Incident counts. The number of data security incidents, customer complaints, or safety events tolerated before a mandatory review.
SLA penalties and uptime targets. For technology companies, this usually means a maximum acceptable downtime or penalty exposure per quarter.
Federal Reserve supervisory guidance makes the point that an effective risk appetite statement needs enough detail for the chief risk officer and independent risk functions to set firm wide limits from it. If your statement is too abstract for your CRO or general counsel to turn into a number, it needs more work before the board signs it.
A significant share of risk programs fail at the aggregation step, where individual unit level risks get rolled up into a single enterprise view. COSO’s detailed ERM guidance warns against naive aggregation and recommends defining your method upfront, whether that is a worst case percentile, a value at risk style band, or a documented scenario stress test, so auditors and examiners can reproduce your numbers later.
The aggregation problem is also a double counting problem. If your sales team tracks customer concentration risk and your finance team separately tracks revenue concentration risk, make sure you are not reporting the same exposure twice under two different labels. Pick one owner per risk category and one clear definition.
Monitoring frequency should match how fast the risk can move. Cyber and liquidity risks often need weekly or even daily dashboards. Strategic and reputational risk can usually tolerate a quarterly look. Build an exception report template now, before you need it: date, business unit, threshold breached, amount over limit, proposed remedy, and sign off authority.
Sample language your board can actually use
Abstract advice is easy to nod along to and hard to apply at 4:45 PM before a board meeting. Here are three short templates you can edit directly.
A corporate level statement, concise enough for the first slide of a board deck: “The company pursues growth through disciplined expansion and accepts moderate operational and financial risk in doing so. The company has low appetite for legal, regulatory, and reputational risk, and will not pursue revenue opportunities that create material compliance exposure.”
Compliance maintains zero tolerance for unresolved regulatory filings beyond their statutory deadline."
An innovation and cyber template, useful for fast moving product teams: “Engineering may pilot new technologies, including AI tools, under legal review, provided any customer data exposure risk is assessed before launch. The company has low tolerance for unencrypted storage of personal data and treats any confirmed breach as an immediate board notification event.” You can see our AI governance page for more on building tolerance language around AI specific risk, an area that is moving faster than most board policies can keep up with.
Cascading these from the top level statement down to department KPIs is the part most companies skip. The table below shows how one corporate level theme breaks into a unit level tolerance and a metric someone actually watches.
Corporate theme | Unit level tolerance | Monitoring metric |
|---|---|---|
Low legal and regulatory risk | Zero unresolved statutory filings past deadline | Count of late filings per quarter |
Moderate operational risk | Uptime at or above 99.5% | Hours of downtime per month |
Low data security risk | No unencrypted storage of personal data | Number of confirmed security incidents |
Once the tolerance and metric exist, the reporting line writes itself: who collects the number, how often, and who gets told when it crosses the line.
Who approves it and how often should the board review it
The board approves the risk appetite statement. That is not a drafting nicety, it is the governance line regulators draw. A 2023 FDIC speech on corporate governance states plainly that the board holds ultimate responsibility for approving risk appetite, while senior management operationalizes it day to day, including maintaining the risk governance structure underneath it.
In practice, that division of labor looks like this:
The board approves the statement, challenges management’s proposed tolerances, and reviews aggregate exposure against those tolerances at every regular meeting.
The CEO and CRO (or equivalent senior leader) translate the statement into limits, dashboards, and escalation paths, and report breaches promptly rather than waiting for the next scheduled meeting.
Business unit leaders operate within the cascaded tolerances and are the first line of defense, flagging exceptions before they become breaches.
That first, second, and third line of defense structure, with business units owning risk day to day, a risk or compliance function monitoring it independently, and internal audit checking both, is the same three line of defense model the FDIC’s guidance expects boards to maintain for larger, complex institutions. Smaller companies rarely need the full formal structure, but the separation of duties behind it, someone doing the work, someone checking the work, someone auditing the checking, scales down just fine.
On cadence, treat the annual review as your baseline, not your ceiling. Review the full statement at least once a year, and revisit specific tolerances quarterly if your business or market is volatile. FDIC speeches and proposed guidelines have recommended quarterly review for larger, more volatile institutions, with documented evidence of breach remediation available for examiners. Trigger an immediate review, outside the normal calendar, whenever you enter a new market, close a material acquisition, or face a regulatory inquiry.
Communicating the statement and handling breaches
A risk appetite statement that lives only in the board portal is not doing its job. It needs to reach the people making daily decisions, and it needs a clear path for what happens when someone crosses the line.
Communicate it in context, not as a memo. Build the relevant tolerance into the training, dashboard, or approval workflow each team already uses, rather than circulating a standalone PDF nobody reopens.
Define breach detection before you need it. Decide in advance who is responsible for noticing a tolerance breach: automated system alerts for metrics like uptime, manual review for judgment calls like reputational exposure.
Set a reporting template and a clock. A breach report should capture what happened, which tolerance it violated, the business impact, and the proposed fix, with a defined window for escalation to the board.
Document the exception, not just the incident. If management grants a temporary exception to a limit, write down who approved it, why, and for how long, because that record is what an examiner or acquirer will ask for later.
Pro Tip: Keep a running log of every exception and breach, resolved or not. It is the single most persuasive document you can hand a regulator, auditor, or acquirer’s diligence team.
This documentation habit matters well beyond routine compliance. If a breach ever triggers a formal internal investigation, the quality of your existing records determines how fast and how credibly you can respond. Our piece on cross border internal investigations covers the documentation gaps that most often turn a manageable incident into a prolonged one. The same look back evidence standard applies to operational resilience questions, which our business continuity overview addresses from the continuity planning side.
Why most risk appetite statements end up as shelfware
I have read a lot of risk appetite statements that were beautifully written and never used again after the board meeting where they were approved. The usual cause is not bad drafting. It is that nobody assigned ownership for keeping the statement connected to real decisions.
An embedded legal function can close that gap because it sits close enough to the business to notice when a decision is about to test a tolerance, not just after the fact. That means drafting the statement with management instead of handing down generic language, building the cascade into department level policies, and maintaining the breach and exception log that examiners and acquirers eventually ask to see.
Boards and regulators tend to look for the same tangible artifacts:
A signed, dated board resolution approving the statement.
A cascaded set of department level tolerances tied to the top level language.
A breach and exception log with resolution dates.
Evidence the board actually reviewed the statement on its stated cadence, not just once at adoption.
If you cannot produce all four on short notice, the statement is policy in name only.
Putting it on one page for your board
Your board does not want a thirty page risk report. It wants a page it can absorb in the time it takes to pour coffee.
Lead with your one sentence appetite statement, the same language the board approved. Underneath it, list three supporting metrics that show the statement in action: one financial, one operational, one legal or regulatory, each with its current value against its tolerance.
Attach three short annexes: the full tolerance table, the current escalation path with named owners, and a brief list of recent breaches or changes since the last review. That is the whole memo. Boards approve faster and ask sharper questions when the document respects their time, and a sharper board conversation is usually the difference between a statement that gets used and one that gets filed.
— Amy Natasha Osteen
Getting your statement from draft to board ready
Writing a risk appetite statement is not hard. Writing one that survives contact with a real board meeting, a regulator’s request, or an acquirer’s diligence team is a different project, and it is the project most companies underestimate.
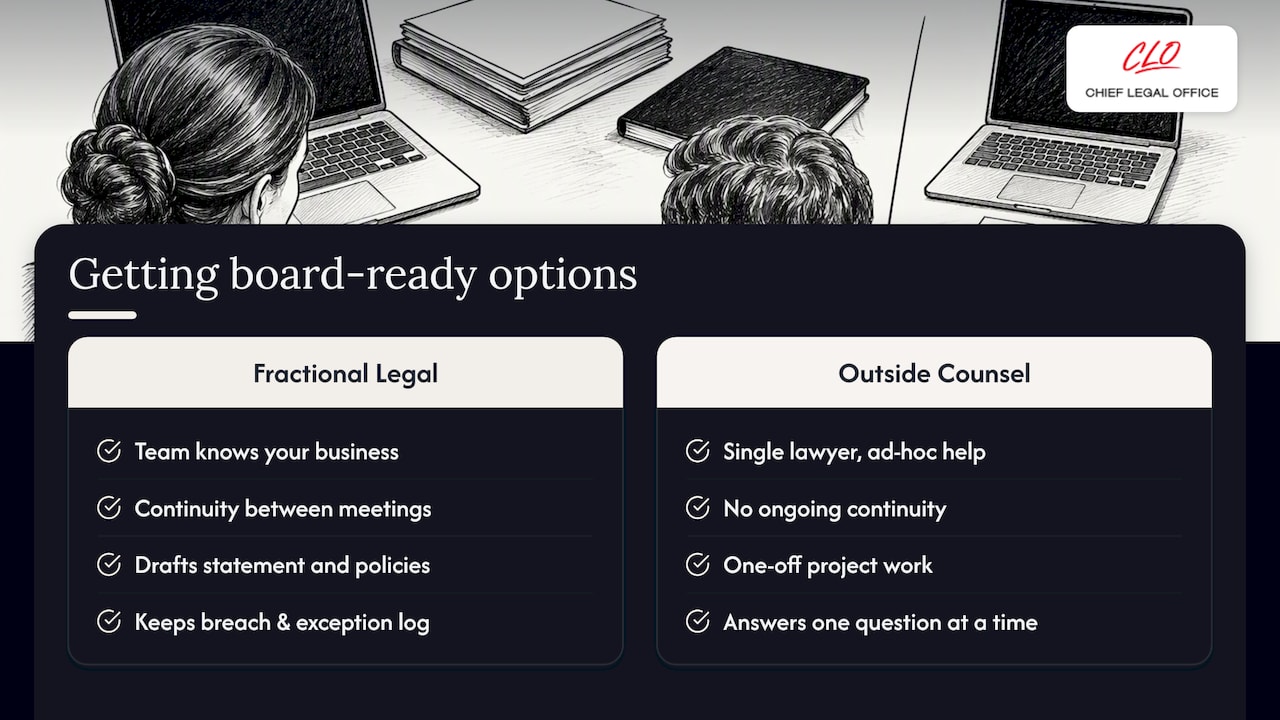
This is exactly the kind of work a fractional in house legal department is built for. Instead of a single outside lawyer answering one question at a time, you get a team that already knows your business well enough to draft the statement, cascade it into department policies, and keep the breach and exception log current between board meetings. That continuity is the real difference from hiring outside counsel for a one off project: the people who wrote your tolerances are still there when a business unit asks for an exception six months later.
A fractional in house legal department builds that structure around companies that have outgrown ad hoc legal support but are not yet ready for a full time General Counsel. If your board needs a risk appetite statement before the next meeting, or a regulator has asked you to document your governance process, our Fractional General Counsel service can own that drafting and the ongoing review cadence behind it. Companies working through a capital raise often need this governance work done in parallel with diligence, which our Capital Raises and M&A team handles directly. For businesses operating in higher scrutiny spaces such as digital assets, where appetite language has to connect to specific regulatory exposure, our partner resource on crypto securities compliance is a useful companion read.
Plans start at the Foundations tier for $1,000 per month, scaling up to Embedded Access and Strategic Growth as your governance needs grow. If you want a specific, defensible risk appetite statement on your board’s desk before the next meeting, get in touch and we will tell you exactly what that looks like for your company.
This article is general information, not a substitute for advice from a qualified financial advisor. Consult a qualified financial professional about your own circumstances before acting on anything here.
FAQ
What is an example of a risk appetite statement?
A typical corporate level example reads: “The company pursues growth through disciplined expansion and accepts moderate operational and financial risk, while maintaining low appetite for legal, regulatory, and reputational risk.” Unit level statements get more specific, tying that language to measurable tolerances like uptime targets or filing deadlines.
What are the levels of risk appetite?
Most organizations use qualitative bands such as low, moderate, and high appetite for each risk category, rather than a fixed universal scale. COSO’s guidance recommends pairing these bands with cascaded, quantified tolerances as a program matures, since a label alone does not tell a manager where the line sits.
Who approves the risk appetite statement?
The board approves the risk appetite statement, while senior management, often led by the chief risk officer, operationalizes it into limits and reporting. A 2023 FDIC speech confirms this division: ultimate approval authority sits with the board, and day to day governance sits with management.
How do you calculate risk appetite?
There is no single formula. Organizations typically start with a qualitative appetite statement per risk category, then translate it into financial loss bands, capital ratios, or incident thresholds that management can track monthly. Federal Reserve guidance stresses that the statement needs enough detail for the risk function to set firm wide limits directly from it.
What is the difference between risk appetite and risk tolerance?
Risk appetite is the broad, strategic statement of how much risk an organization will accept in pursuit of its goals. Risk tolerance is the tactical, measured version of that appetite, expressed in the actual units of the objective, as explained in Wolters Kluwer’s comparison.
Sources
Recommended
The lawyerly fine print: This article is for general information, not legal advice…